Don't trust this. The reel's picture of events is not reliable. The project is real and does autonomous local pentesting on a phone.
- No record found: The sources reviewed do not settle whether Knightcrawler is an autonomous agent that runs on a phone.
- No record found: The sources reviewed do not settle whether Knightcrawler scans the network for smart TV, smart locks, cameras, basically anything your network is…
- No record found: The sources reviewed do not settle whether Knightcrawler covers its path by going to Instagram and stuff to seem like a legit user.
- No record found: The sources reviewed do not settle whether Knightcrawler tries to knock on as many ports it can find.
Checked against: GitHub
Why we say that›
Knightcrawler runs real offline pentesting on a phone but uses a 1.2B model, not 2B Qwen, and does not visit Instagram.
The core idea of an autonomous, fully local penetration testing agent on a smartphone that discovers hosts, finds vulnerabilities and produces reports without internet is accurate and confirmed by the project's GitHub and discussions. Several specific technical claims are overstated or wrong — the model size and name, the Instagram stealth method, and the level of autonomous exploitation. The Watch Dogs comparison is for hype. Local networks can be scanned offline if the phone is placed on them, and it can attempt WiFi cracking in some modes.
The project is real and does autonomous local pentesting on a phone. The specific model details, Instagram cover story, and game-like universal hacking portrayal do not match the actual code or documentation.
The on-screen demo and screenshots are from the real project but show a specific test network. Real-world performance varies and the model succeeds on only about 50% of commands on first try.
Reported 14 Aug 2026
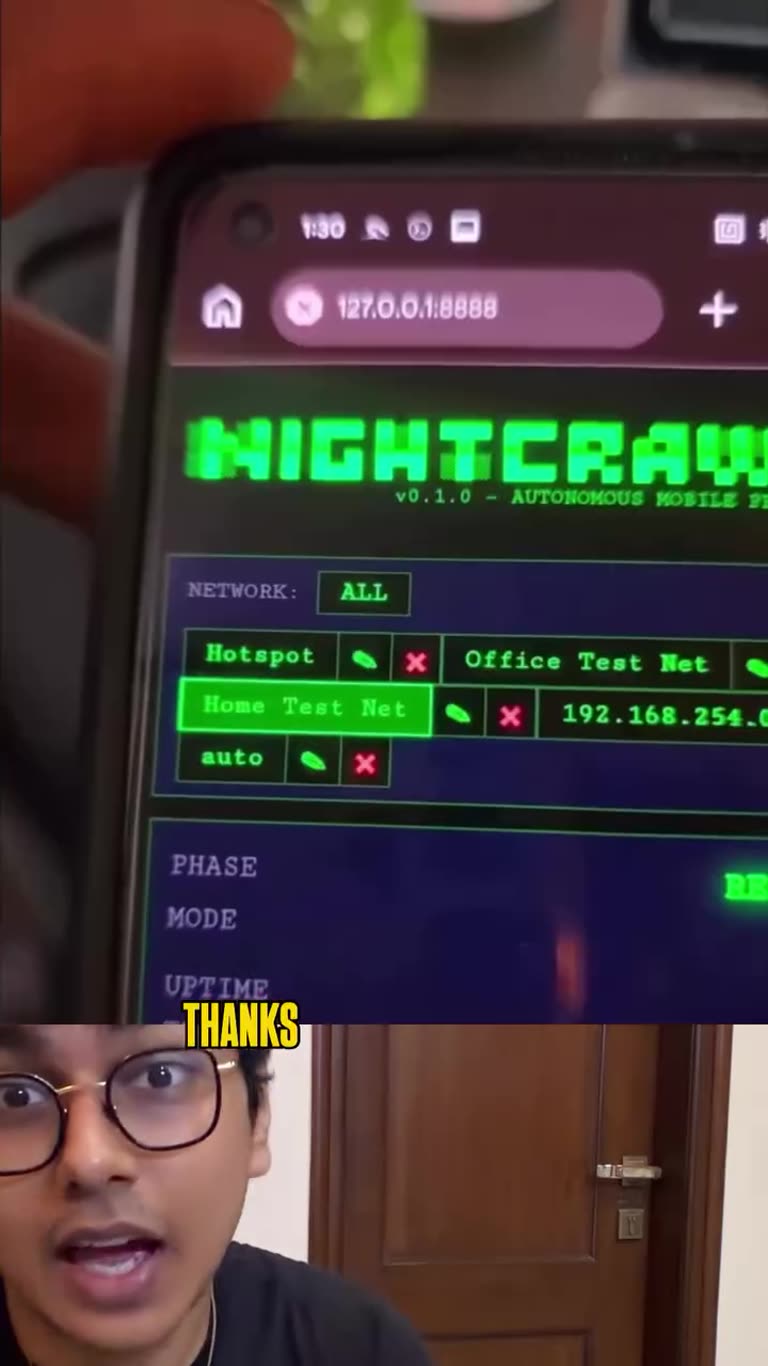
Claims
1 true · 9 no record
- No record found
Knightcrawler is an autonomous agent that runs on a phone
What we found
It is an autonomous penetration testing agent designed to run entirely on a smartphone using Kali NetHunter. Drop the phone on the network and it works without further input.
- No record found
Knightcrawler scans the network for smart TV, smart locks, cameras, basically anything your network is connected to and finds the vulnerabilities in them
What we found
It discovers hosts, maps services, checks for default credentials and known vulnerabilities using playbooks and a CVE database.
- No record found
Knightcrawler covers its path by going to Instagram and stuff to seem like a legit user
What we found
No mention in GitHub, CLAUDE.md, HN thread or related posts of visiting Instagram or mimicking users on social media. It uses slow scanning rates and host rotation for stealth.
- No record found
Knightcrawler tries to knock on as many ports it can find
What we found
It maps services and probes ports as part of standard network discovery and vulnerability scanning.
- No record found
Knightcrawler uses a local 2,000,000,000 parameter Qwen model fully offline
What we found
It uses a local 1.2B-parameter LFM2.5-1.2B-Instruct-Heretic model, not Qwen and not 2 billion parameters.
- No record found
Knightcrawler does not have to be connected to the Internet or to the hacker's network
What we found
It runs entirely offline with no cloud connectivity required. All inference and operations are local to the phone.
- No record found
Knightcrawler is a pen testing tool that stops at testing for vulnerabilities and provides a detailed report of the vulnerabilities found
What we found
It is explicitly a penetration testing tool that discovers hosts, maps services, tests for vulnerabilities and generates a structured report. It includes safety layers and requires rules of engagement.
- No record found
The Knightcrawler code is open source
What we found
The full project is publicly available on GitHub with code, documentation and discussion on Hacker News.
- No record found
Knightcrawler can crack the WiFi password if you don't have it
What we found
It has a WiFi breach mode that can autonomously crack WPA2 in some setups using a USB adapter, but this is one optional capability, not a core or guaranteed function for every network.
- True
local networks without internet are also unsafe
What we found
The tool is specifically designed to test air-gapped or offline local networks by physically placing the phone on them.
The full story, from the sources›
An autonomous penetration testing agent that runs entirely on a smartphone. Drop the phone on a network, walk away, and it discovers hosts, maps services, finds vulnerabilities, and generates a pentest report — all without cloud connectivity. - GitHub (2026-08-03)
From primary sources
What else it leaves out (2)›
- It requires a rooted Android phone with Kali NetHunter, a scope-enforcement proxy for safety, and signed rules of engagement before use on any target.
- The tool is for authorized pentesting only and is not a magical universal hacker device as the Watch Dogs comparison suggests.
How it's framed (4)›
About this account›
- The account posts tech hype and cool gadget videos, often drawing pop-culture comparisons like Watch Dogs to generate interest.
Checked against 1 source · 14 Aug 2026
Help us improve
Was this analysis useful?
One tap helps us find what Blindspot should improve next.